Credentials for GCP GKE
You can fully automate the provisioning and ongoing lifecycle management of GKE clusters in all supported Google Cloud regions.
You can have a GKE cluster operational in just a few simple steps. To do this, you need to provide credentials to GCP that will provide the controller with programmatic access using GCP's APIs.
Create Cloud Credential
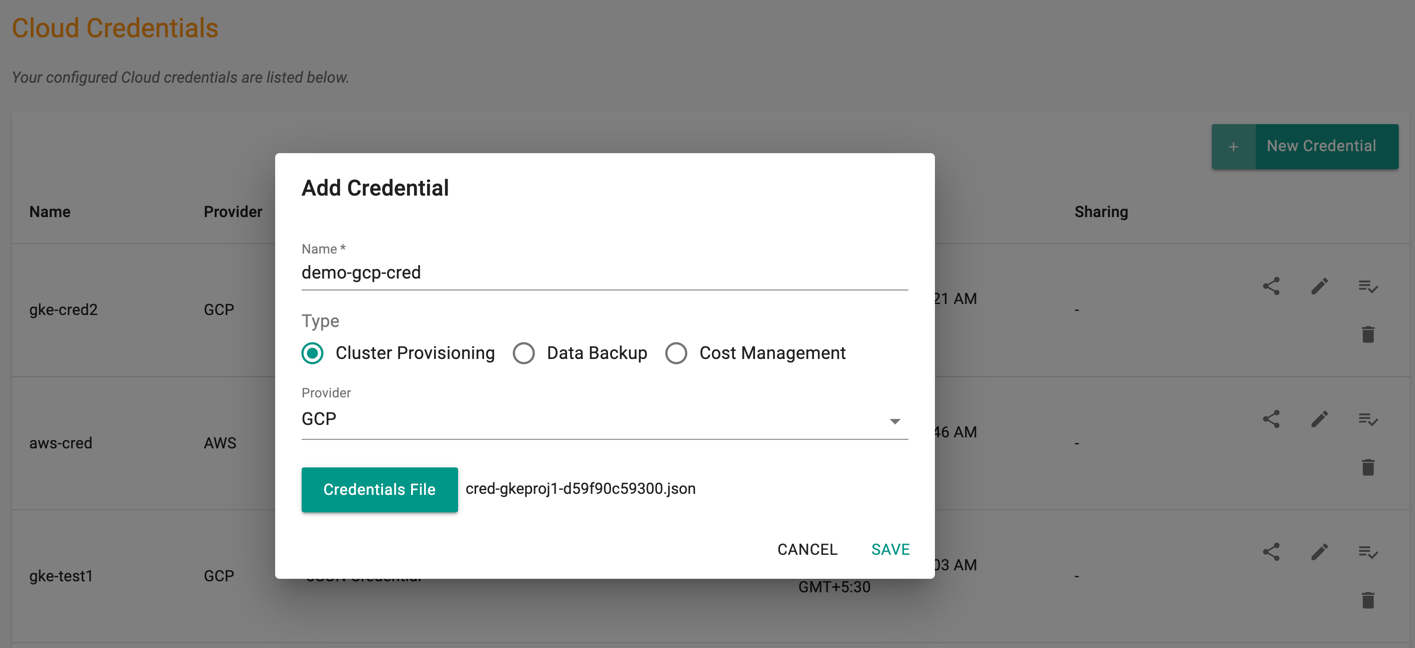
- Login to the Web Console and select Cloud Credentials under Infrastructure
- Click New Credential and provide a unique name
- Select the Type Cluster Provisioning and Provider GCP
- Click Credentials File and upload the json credentials file from your system. - Click Save
Important
Refer GCP Cloud Credential Setup to learn how to get the credential JSON file from the GCP console.
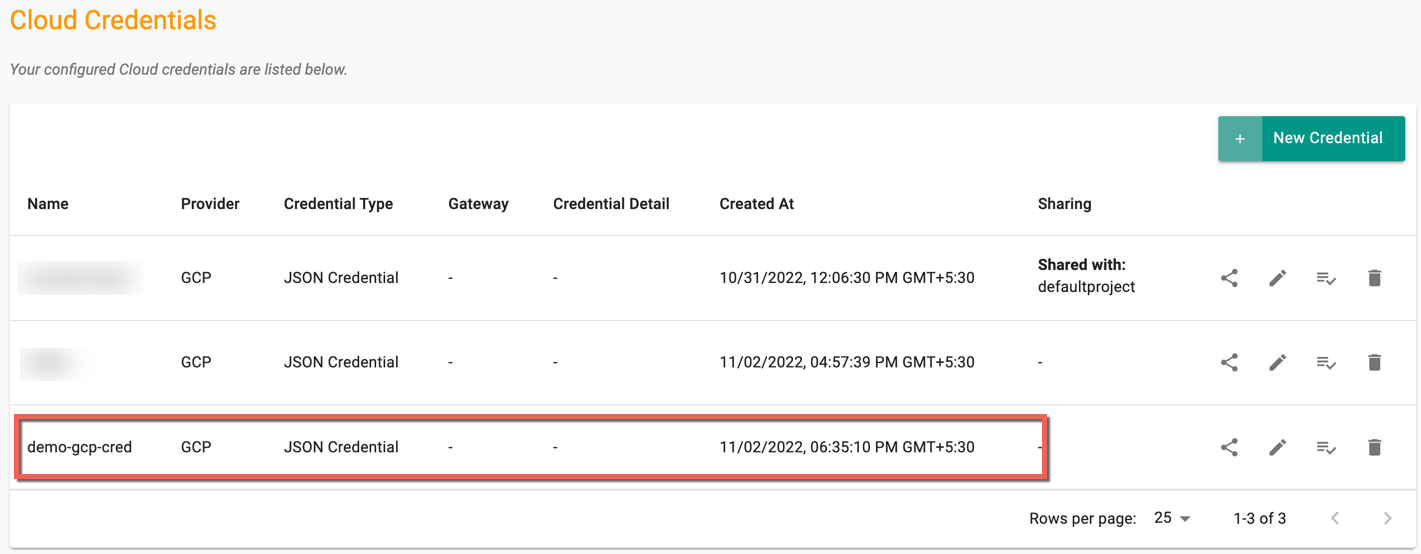
On successful creation, you can view the details of the newly created "cloud credential". An example is shown below.
View Credentials
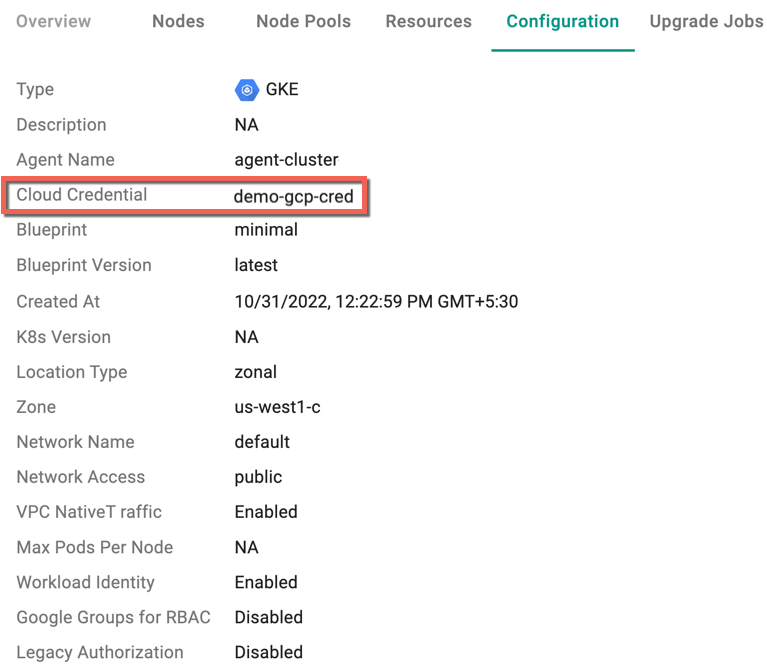
Navigate to the "Cluster->Configuration" tab to view the "cloud credential" currently being used by the cluster.
Day-2 Updates
When you replace the service-account JSON on a GCP credential that clusters already use, Rafay saves the new key immediately. Clusters keep the previous key until the next cluster operation (upgrade, scale, node pool change, or delete). That next operation writes the latest saved key before talking to GCP.
Previously, clusters kept only the key from provision time, so the next upgrade, scale, or delete often failed with a GCP authentication error.
Update from Cloud Credentials
- Go to Infrastructure → Cloud Credentials
- Edit an existing GCP JSON credential and click Save
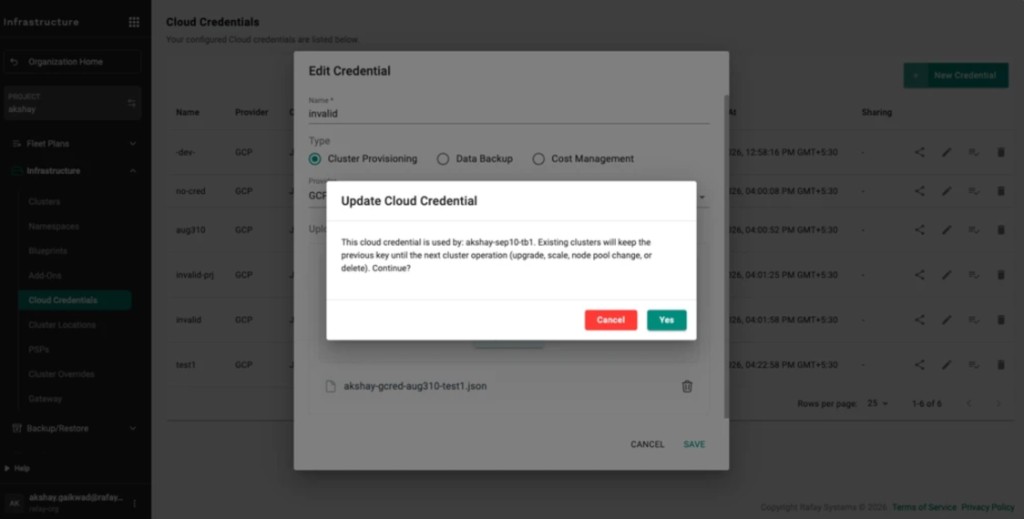
- If any clusters use the credential, confirm the dialog:
This cloud credential is used by: cluster-a, cluster-b. Existing clusters will keep the previous key until the next cluster operation (upgrade, scale, node pool change, or delete). Continue?
Note
rctl and Terraform do not show this in-use warning when you update a GCP credential. The console does.
Switch the credential on a cluster
You can also change which cloud credential a cluster uses from the cluster Configuration tab.
- Open the cluster and go to the Configuration tab
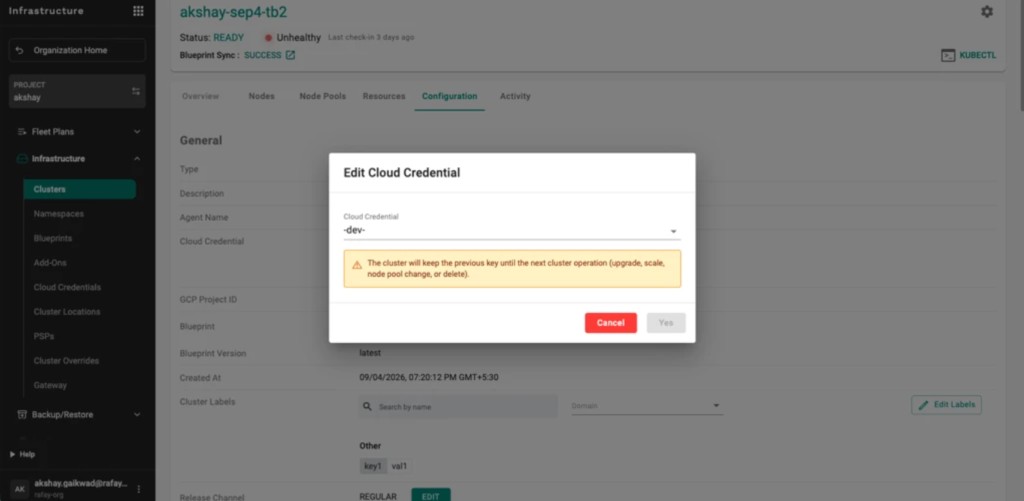
- Click Edit under Cloud Credential
- Select a different credential, then click Yes
The dialog warns that this cluster keeps the previous key until the next operation. Yes stays disabled until you pick a different credential. The picker waits for the credentials list (spinner), then shows names.
Edit is disabled while a cluster operation is in progress:
Cluster operation is in progress, please wait until it completes.
Delete a credential that is in use
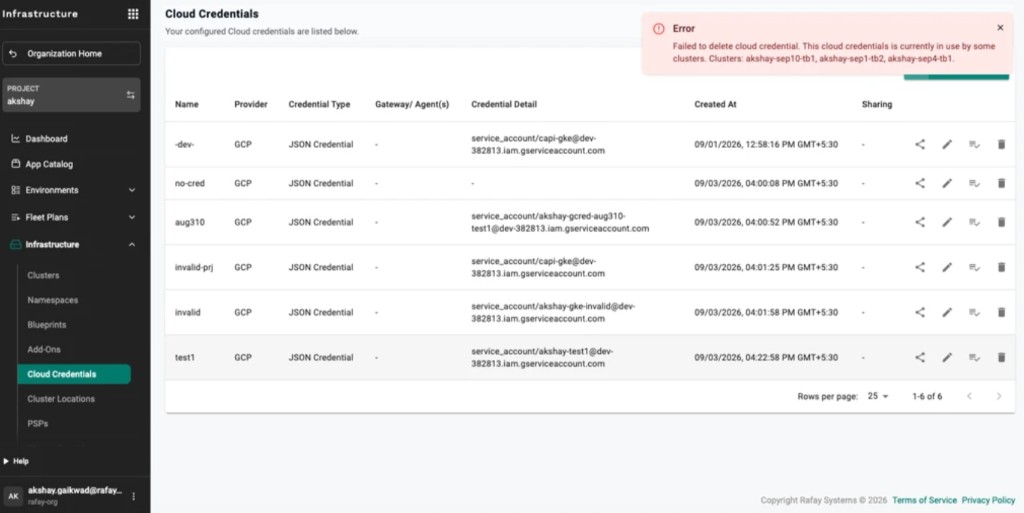
Deleting a GCP credential that clusters still use continues to fail. The error now names those clusters:
Failed to delete cloud credential. This cloud credentials is currently in use by some clusters. Clusters: cluster-a, cluster-b.
Share Credentials
Organizations can create and use "unique" cloud credentials per project. This approach can be useful if different cloud provider accounts need to be used in every project. This helps with "billing" and "isolation".
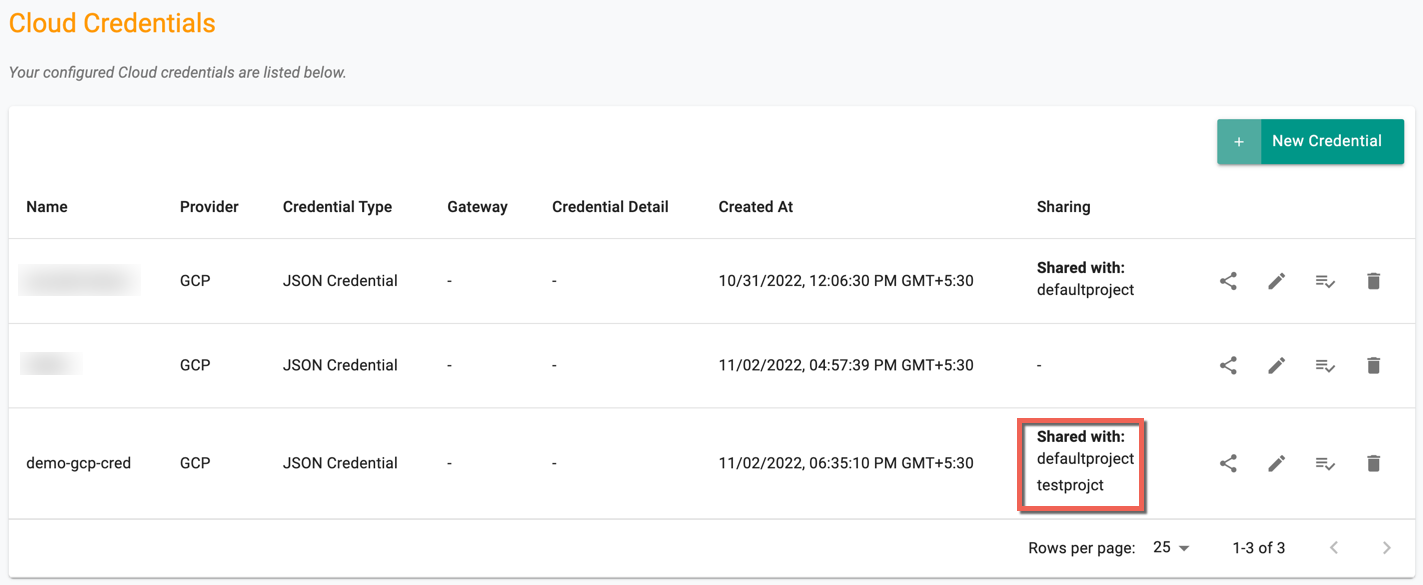
However, this approach may not be practical for scenarios where the organization's security policies may require "centralization" of cloud credentials. For scenarios like this, organizations can "share" their cloud credentials with "select" or "all projects".
- Click on the "share" menu option
- Select the projects you would like to share the cloud credential with
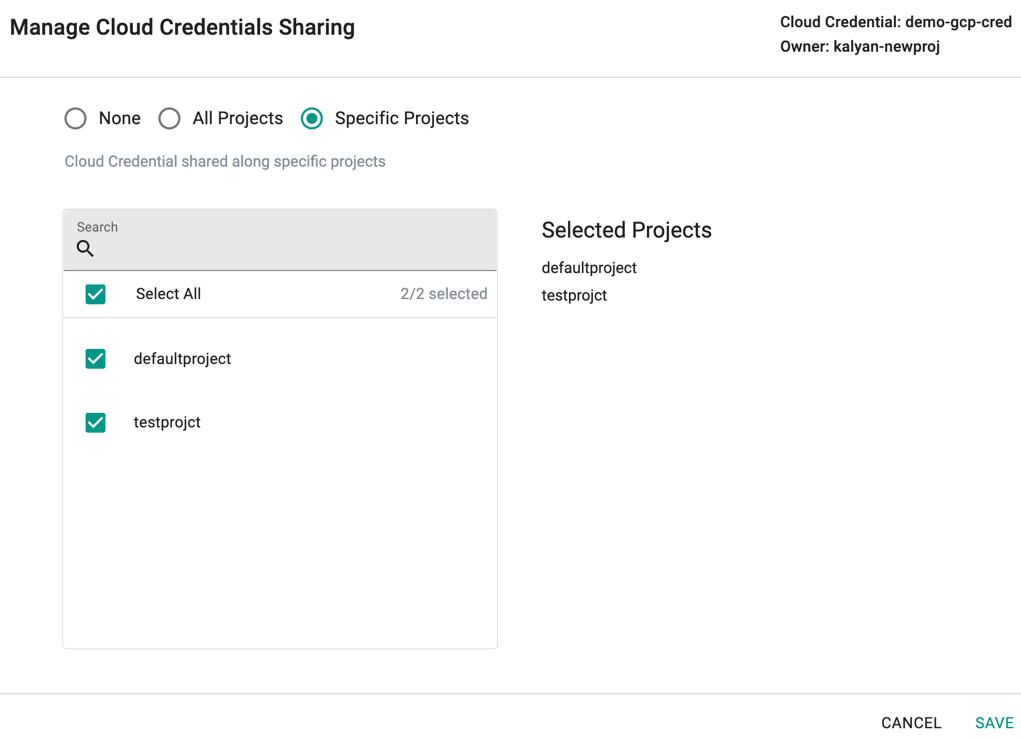
The downstream projects that "inherit" the shared cloud credential can view and use the inherited cloud credentials. But, they are not allowed to edit/delete them.